
Your sales team is in a meeting. A prospect is on the screen. The rep opens Salesforce to pull up the account history – and the page takes eight seconds to load.
That is not a Salesforce problem. It is a network architecture problem that shows up as a Salesforce problem.
In 2026, Salesforce will be the operating system of commercial enterprise. CRM records, pipeline visibility, service case management, marketing automation, Revenue Cloud, Einstein AI analytics – businesses have consolidated their most revenue-critical workflows into a platform that sits entirely outside the corporate network, hosted on Salesforce’s global infrastructure, accessed through a browser from hundreds of branch locations and thousands of remote endpoints every hour of every working day.
And for organizations still routing that traffic through legacy network architectures – MPLS circuits, central inspection stacks, backhauling through data centers that add latency with every hop – the performance gap between what Salesforce is capable of and what users actually experience is wide, measurable, and entirely fixable.
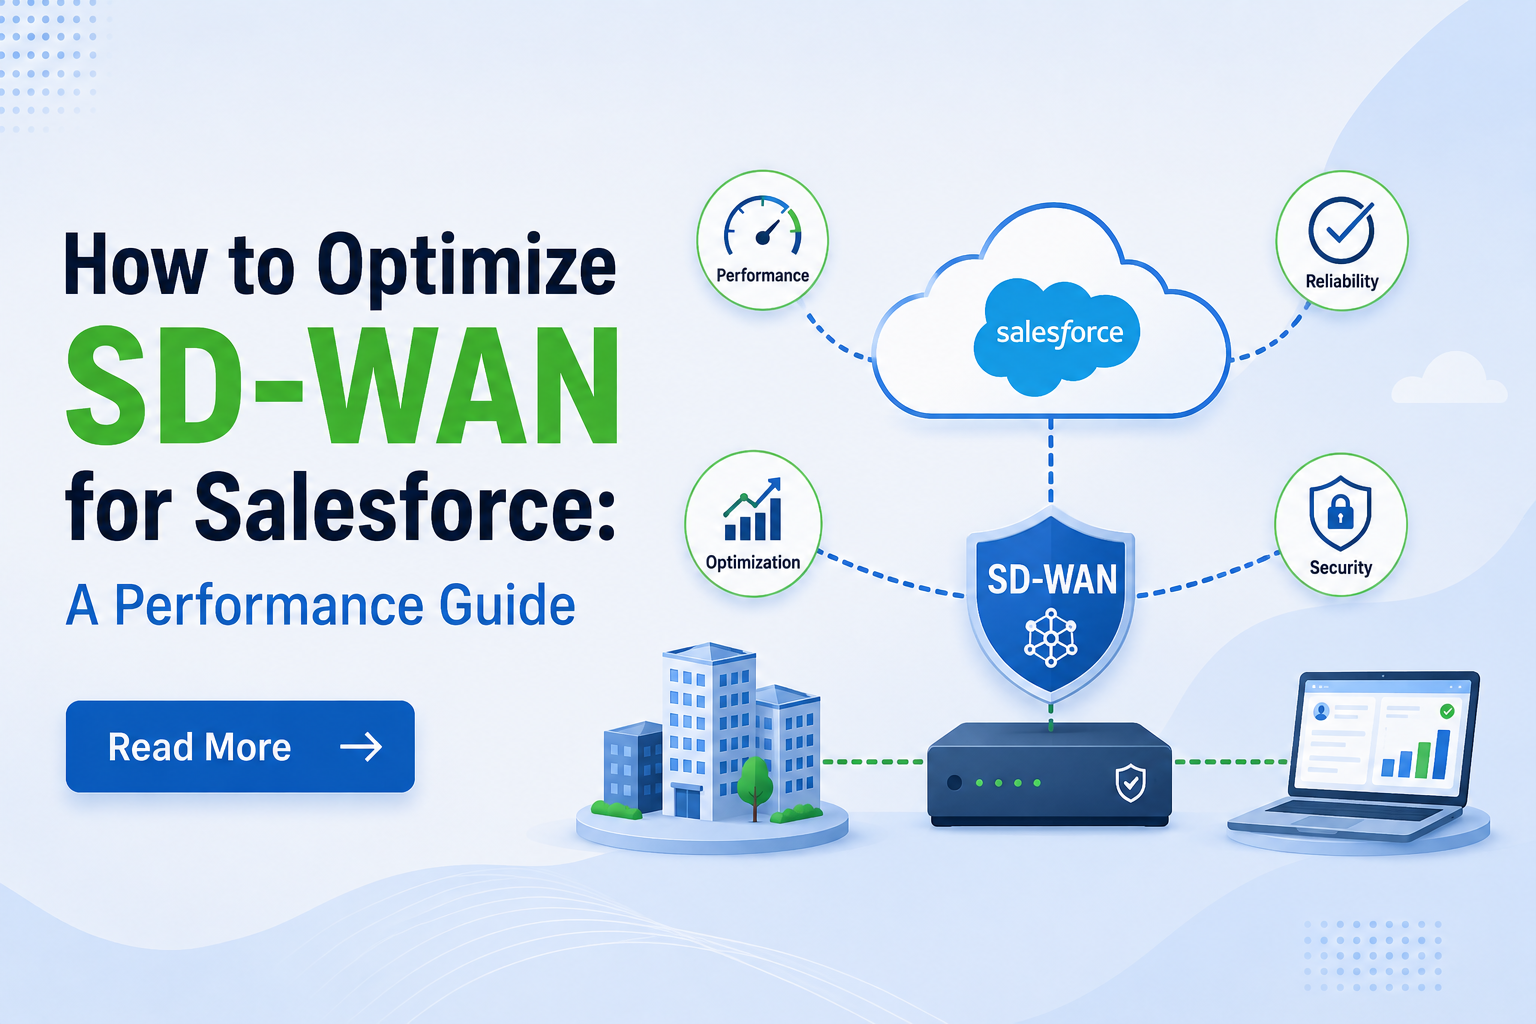
SD-WAN is the fix. But not all SD-WAN deployments are equal in what they deliver for Salesforce specifically. This guide explains the architecture, the optimization techniques, and the platform that delivers the best result.
Why Salesforce Is Uniquely Sensitive to Network Conditions
Understanding why Salesforce demands specific network treatment requires understanding how the application actually works – because Salesforce is not a simple SaaS application in the way that, say, a static documentation site is.
Salesforce’s front door – salesforce.com and login.salesforce.com – is hosted in a data center local to the user. However, the serving host may be regions or continents away. The farther the distance between an end-user and the host, the more performance degrades due to multiple hops, congestion, latency, and packet loss.
This geographic routing complexity is compounded by Salesforce’s architectural characteristics. Salesforce relies on heavy use of JavaScript and Cascading Style Sheets, so page sizes are large and expanded further by popular plugins – customers use seven plugins on average. Every page load triggers multiple TCP connections, each dependent on round-trip time. Every millisecond of additional latency multiplies across those connections. A 50ms round-trip time produces a markedly different user experience than a 150ms round-trip time – and on a congested internet path, 150ms is conservative.
Leveraging the internet to reach your Salesforce location often leads to slow performance and poor user experience due to the multiple hops each access point must make to reach the destination where the application is hosted. Adding bandwidth will not necessarily help – the quality matters more than the quantity – and technologies such as MPLS and appliance-based WAN optimization tools were not designed for SaaS connectivity and acceleration.
This is the core insight that shapes every Salesforce optimization conversation: more bandwidth is not the answer. The path quality, the number of hops, the proximity to Salesforce’s infrastructure, and the intelligence of the routing mechanism are what determine the experience.
The Five Techniques That Actually Optimize Salesforce Over SD-WAN
Direct Internet Breakout From the Branch
The single highest-impact change most organizations can make for Salesforce performance is eliminating backhauling. When Salesforce-bound traffic from a branch office travels to the corporate data center for security inspection before reaching the internet, every component of that detour adds latency: the WAN hop to the data center, the inspection processing overhead, and the return hop back to the internet to reach Salesforce’s servers.
Traditional architectures that backhaul traffic through a corporate VPN can add crippling round-trip time to Salesforce sessions. A SASE or SD-WAN architecture with direct internet breakout allows Salesforce traffic to exit directly from the branch to the internet – applying security inspection inline at the branch edge, without the round-trip to a central data center.
The latency difference is not incremental. In documented configurations, the difference between centralized breakout and local direct internet access can be a factor of three in round-trip time. A 20ms path to Salesforce.com from a local DIA connection compared to 60ms through a central hub changes the character of the user experience entirely.
First-Packet Application Identification
One of the most consequential technical capabilities in Salesforce optimization is how quickly the SD-WAN platform identifies Salesforce traffic and begins applying the correct routing policy.
Legacy traffic classification reads packet headers and matches on IP address or port number – which works poorly for SaaS applications that use dynamic IPs, shared CDN infrastructure, and HTTPS on port 443 like every other application. By the time the platform identifies the traffic as Salesforce, several packets have already been routed suboptimally.
First-packet application identification classifies traffic as Salesforce from the very first packet – using deep packet inspection, behavioral fingerprinting, and application signature matching – and immediately applies the correct routing policy without the classification latency that affects the first seconds of every new session.
Active and Passive SaaS Path Monitoring
Choosing the best path to Salesforce requires knowing which path is actually performing best at this moment – not which path performed best yesterday, or which path has the highest rated bandwidth.
Active SaaS monitoring proactively measures the performance of all available paths to Salesforce infrastructure using HTTP, ICMP, and TCP probes – measuring round-trip time and packet loss to Salesforce’s specific serving nodes continuously, not just during active sessions. When the active monitoring detects that the local DIA path has lower RTT to Salesforce than the path through the regional hub, traffic is steered locally. When conditions change, the steering changes.
Passive application steering complements this by collecting transport layer and application layer metrics from live Salesforce sessions – measuring actual network and server response times and packet loss in each direction as traffic flows through the network – and incorporating those real-time session metrics into ongoing path selection decisions. The platform learns continuously from actual Salesforce traffic, not just probe traffic.
Forward Error Correction and Packet Duplication
On imperfect internet connections – the real-world condition that most branch offices operate on – packet loss is the primary cause of Salesforce session degradation. When packets are dropped, TCP requires retransmission, which adds delay that compounds with every additional loss event.
Forward Error Correction (FEC) addresses this by proactively sending redundant data alongside primary traffic – allowing the receiving endpoint to reconstruct lost packets from the redundant data without waiting for retransmission. For Salesforce sessions over links with moderate packet loss, FEC can eliminate the retransmission delay that makes pages feel sluggish.
Packet duplication sends the same traffic simultaneously over two different paths – guaranteeing delivery via whichever path arrives first, regardless of which link loses packets on a given segment. For Salesforce traffic on links with unpredictable loss characteristics, packet duplication provides performance consistency that neither FEC alone nor standard path selection can match.
DNS-Aware Traffic Steering
Most SD-WAN Salesforce optimizations focus on the data path – where the TCP traffic flows once the connection is established. DNS steering addresses the step before: ensuring the DNS query that resolves salesforce.com is sent over the same circuit that will carry the subsequent application traffic.
When a branch has two internet links – one from Carrier A and one from Carrier B – and the Salesforce traffic policy prefers Carrier A for SaaS applications, the DNS query for salesforce.com should also go over Carrier A. This ensures the DNS response reflects the routing conditions of the path the actual traffic will use, and that the resolved Salesforce IP addresses are optimal for that carrier’s network topology.
DNS proxy with path-aligned DNS steering coordinates DNS query routing with application traffic steering – eliminating the DNS path mismatch that can route Salesforce sessions through suboptimal network segments despite correct application steering policy.
What the Wrong Architecture Costs in Practice
The business cost of poorly optimized Salesforce performance is measurable in terms that transcend network metrics.
Salesforce’s own research has consistently documented the relationship between page load time and CRM adoption. When loading takes more than three seconds, users begin finding workarounds – offline spreadsheets, email threads, manual notes – that undermine the data quality and pipeline visibility that CRM investment was intended to deliver. At eight to ten seconds per page load, the platform becomes actively counterproductive: sales reps spend more time waiting for Salesforce than using it.
Mission-critical apps like Salesforce demand fast, reliable access regardless of where the user is located. For organizations with distributed sales teams – multiple offices, remote field staff, hybrid workers – the performance baseline that headquarters experiences is rarely what branch offices and remote workers experience. The network architecture that creates excellent Salesforce performance in one location and degraded performance in another is not a Salesforce problem and not a Salesforce solution. It is a network architecture problem that SD-WAN solves.
Why Versa Networks Delivers the Best Salesforce Optimization
Among the SD-WAN platforms available in 2026, Versa Networks provides the deepest and most technically specific implementation of Salesforce optimization – built into the platform architecture rather than configured as an exception.
Versa’s VOS platform includes a dedicated Salesforce-Apps application group in its SaaS application library – a predefined classification set that identifies all Salesforce traffic at the first packet using deep packet inspection up to Layer 7. This is not a generic HTTPS classification that happens to include Salesforce. It is a named, maintained Salesforce application signature that enables IT administrators to create traffic steering policies specifically for Salesforce with the same specificity as a firewall rule.
The active SaaS monitoring implementation is equally specific. Versa’s active monitoring proactively monitors SaaS locations using HTTP, ICMP, and TCP probes, exports the collected metrics to remote sites, and incorporates actively learned metrics into path selection. The platform continuously measures the round-trip time and packet loss from each branch to Salesforce’s serving nodes – and when the local DIA circuit offers lower latency to Salesforce than the central hub path, the SD-WAN policy automatically steers Salesforce sessions through the local connection. In documented configurations, a branch measuring 20ms to Salesforce.com over local DIA compared to 60ms through the central DIA hub will automatically route Salesforce traffic locally- a three-to-one latency improvement with zero manual configuration once the monitoring policy is in place.
Versa SD-WAN steers traffic directly to Salesforce and other SaaS applications using secure local breakout, eliminating the need to backhaul. First-packet identification combined with dynamic path selection and WAN optimization techniques – including Forward Error Correction, packet duplication, and WAN acceleration – delivers low-latency, high-performance access.
The DNS proxy capability aligns DNS query routing with application traffic steering -ensuring that when a policy specifies Salesforce traffic should prefer one circuit over another, the DNS query for Salesforce domain names follows the same path – eliminating the DNS path mismatch that undermines SaaS optimization policies on multi-link branch configurations.
Passive application steering gathers transport layer and application layer metrics from live Salesforce sessions – network response times, server response times, and packet loss in each direction – and uses those real-time session measurements to continuously refine path selection. The platform learns from actual Salesforce traffic behavior, not just from probe traffic that may not reflect the characteristics of production sessions.
Versa also correlates its SD-WAN telemetry with Microsoft Entra security logs to provide visibility into best path selection, risk assessment, and device posture management – extending the observability of Salesforce session performance beyond network metrics into the security posture context that affects access policy.
All of this runs on VOS™ – Versa’s unified operating system – which means Salesforce optimization policy is configured once in the same management console that governs NGFW, ZTNA, CASB, and DLP. There is no separate WAN optimization appliance, no separate SaaS acceleration service, and no additional management interface. The Salesforce performance configuration is part of the network security and routing policy – applied, monitored, and adjusted from a single place.
Also Read: Securing the Modern Manufacturing Network: From Basic LAN to Zero Trust SD-LAN
For organizations that have accepted slow Salesforce as an unavoidable condition of distributed operations – the branch that runs slower than headquarters, the remote rep who works with degraded CRM performance because “that is just how it is from that location” – Versa SD-WAN resolves the problem at the architectural level. Three times lower latency from a local DIA connection. First-packet classification that applies correct routing from session initiation. Active monitoring that continuously selects the best path to Salesforce’s infrastructure. And WAN optimization techniques that protect session quality even on imperfect connections.
That is what Salesforce optimization over SD-WAN looks like when the platform is built for it.

